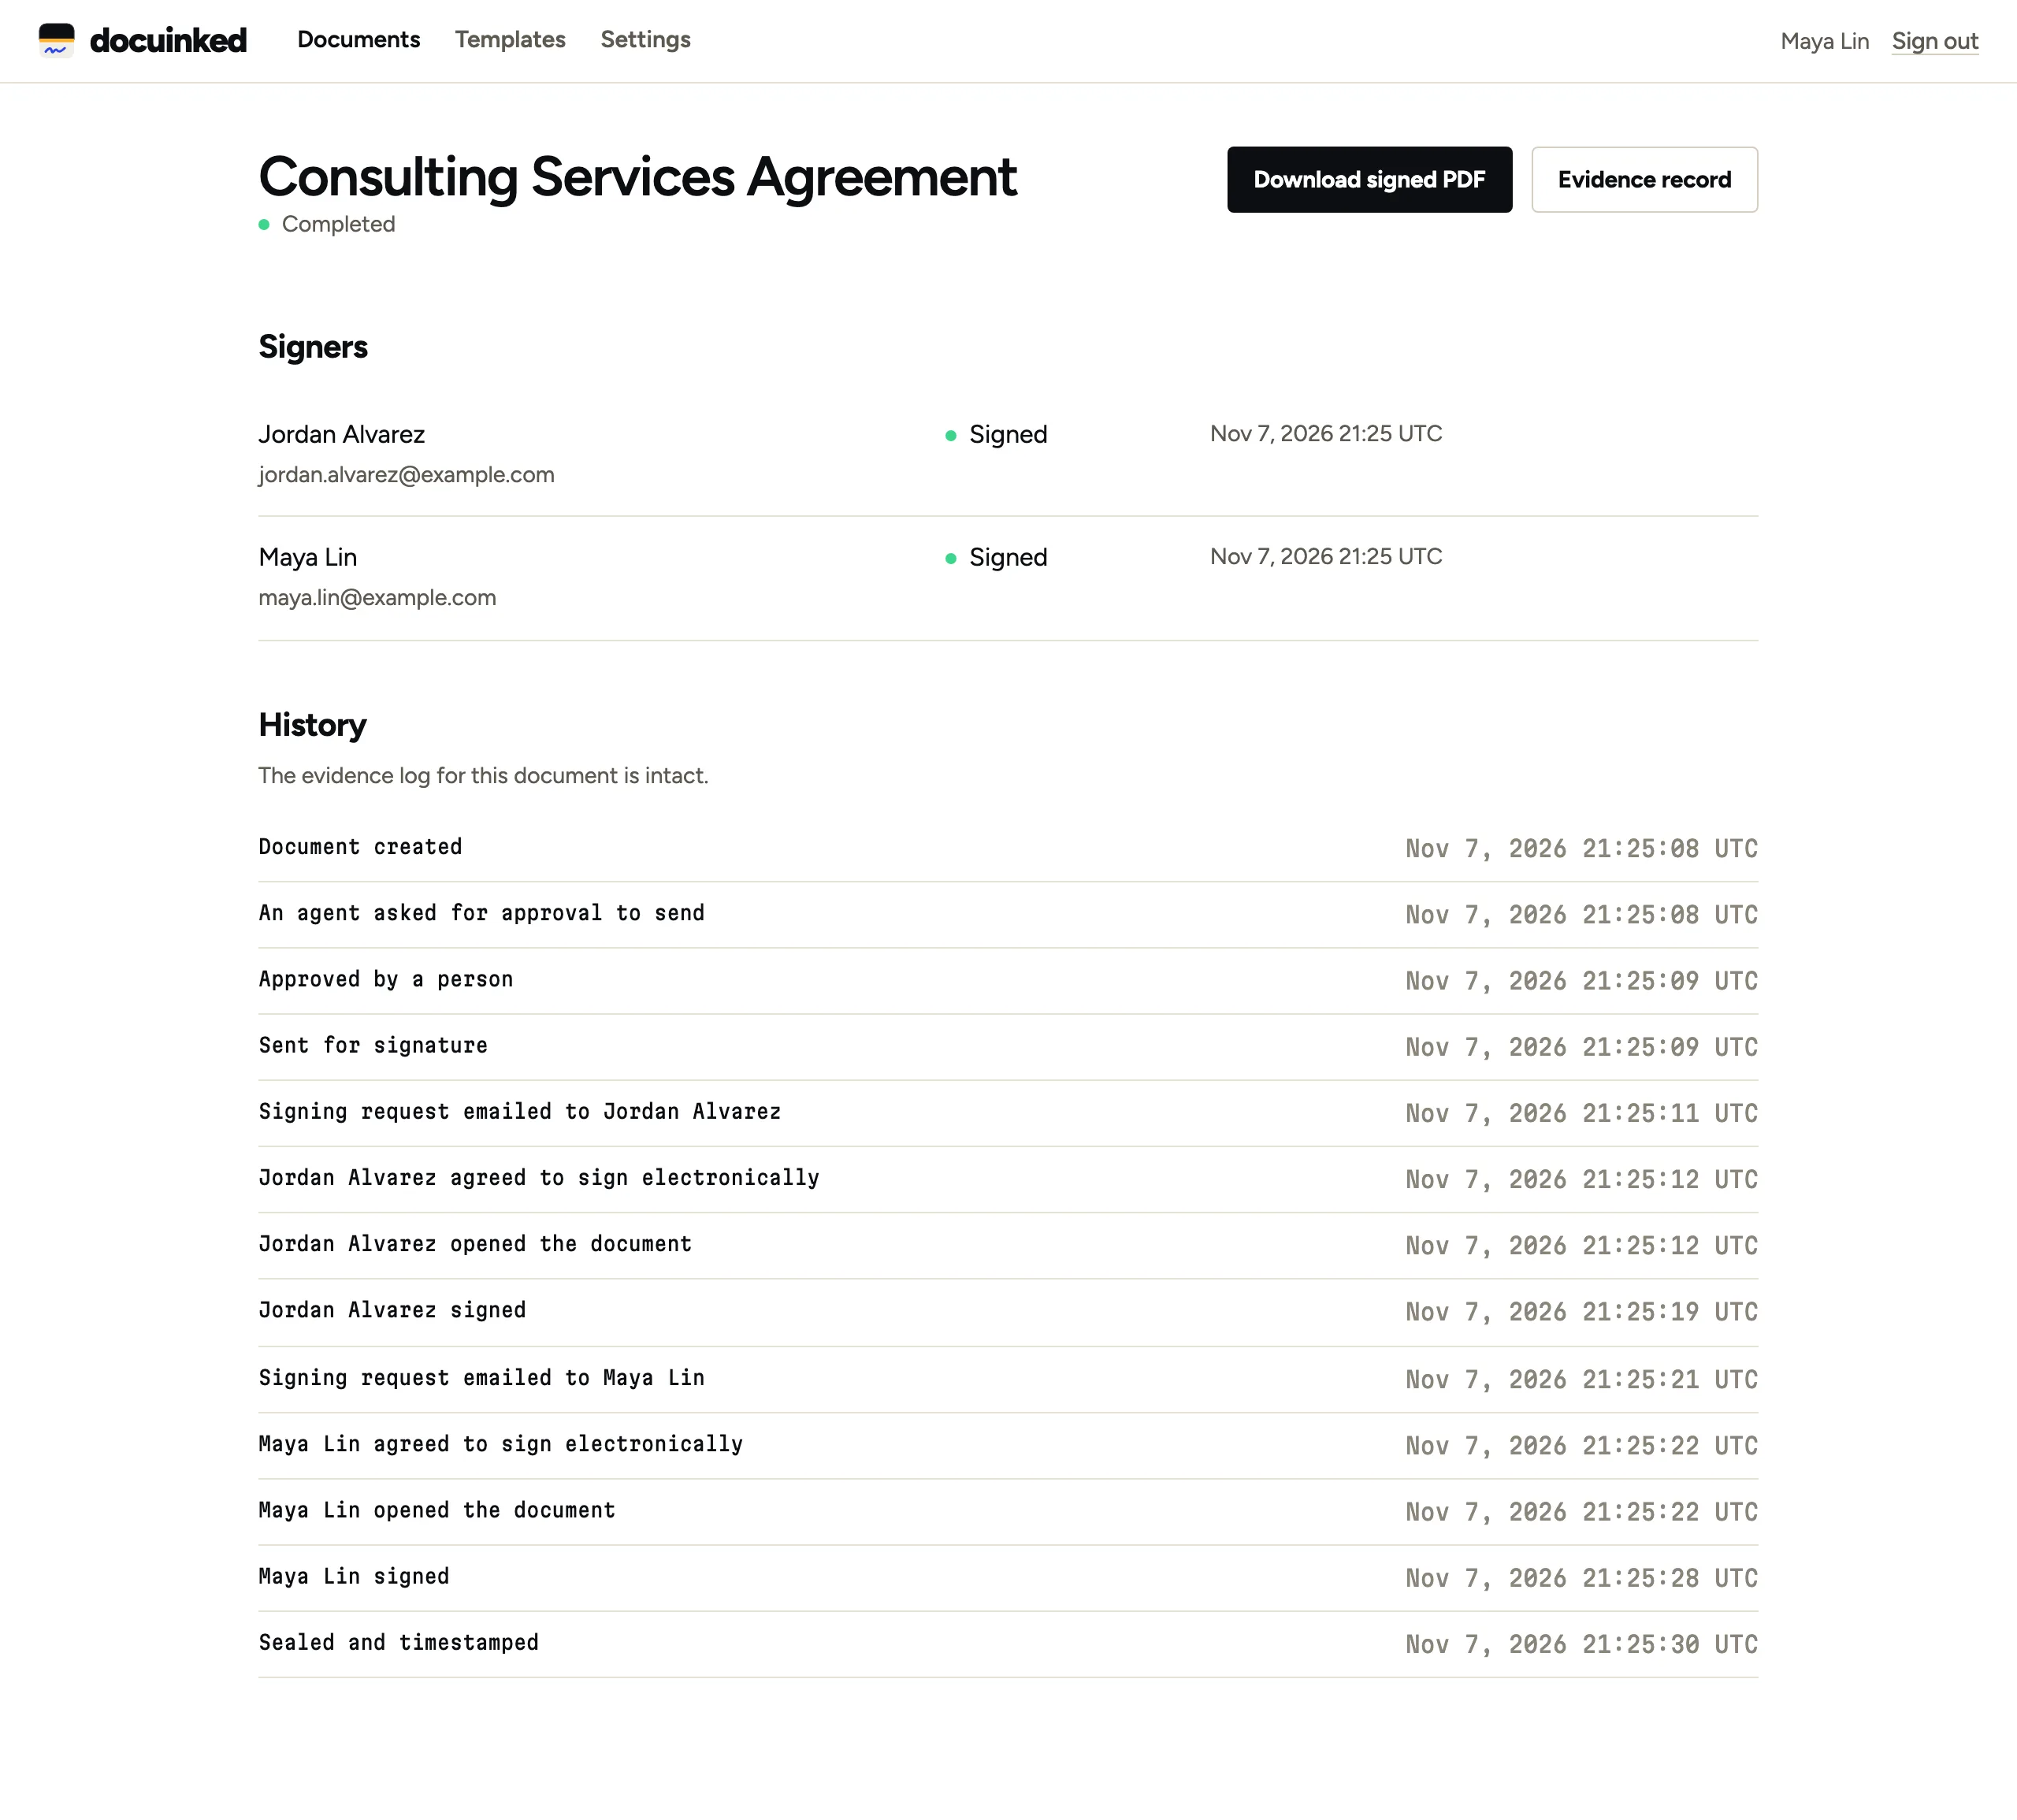
Works with the tools you already use
- Claude
- ChatGPT
- Cursor
- n8n
- Clay
- Zapier
- Make
- Any REST client
Connect by MCP, HTTP or our REST API. Native app listings are coming.
- ESIGN Act and UETA Designed to meet US e-signature law
- Sealed PDF PAdES digital seal on every completed file
- Trusted timestamp Independent RFC 3161 time on every seal
- Full audit trail Every step logged and hash-chained
- Encrypted Documents encrypted at rest with AES-256
One signing layer. Three ways in.
Send it yourself
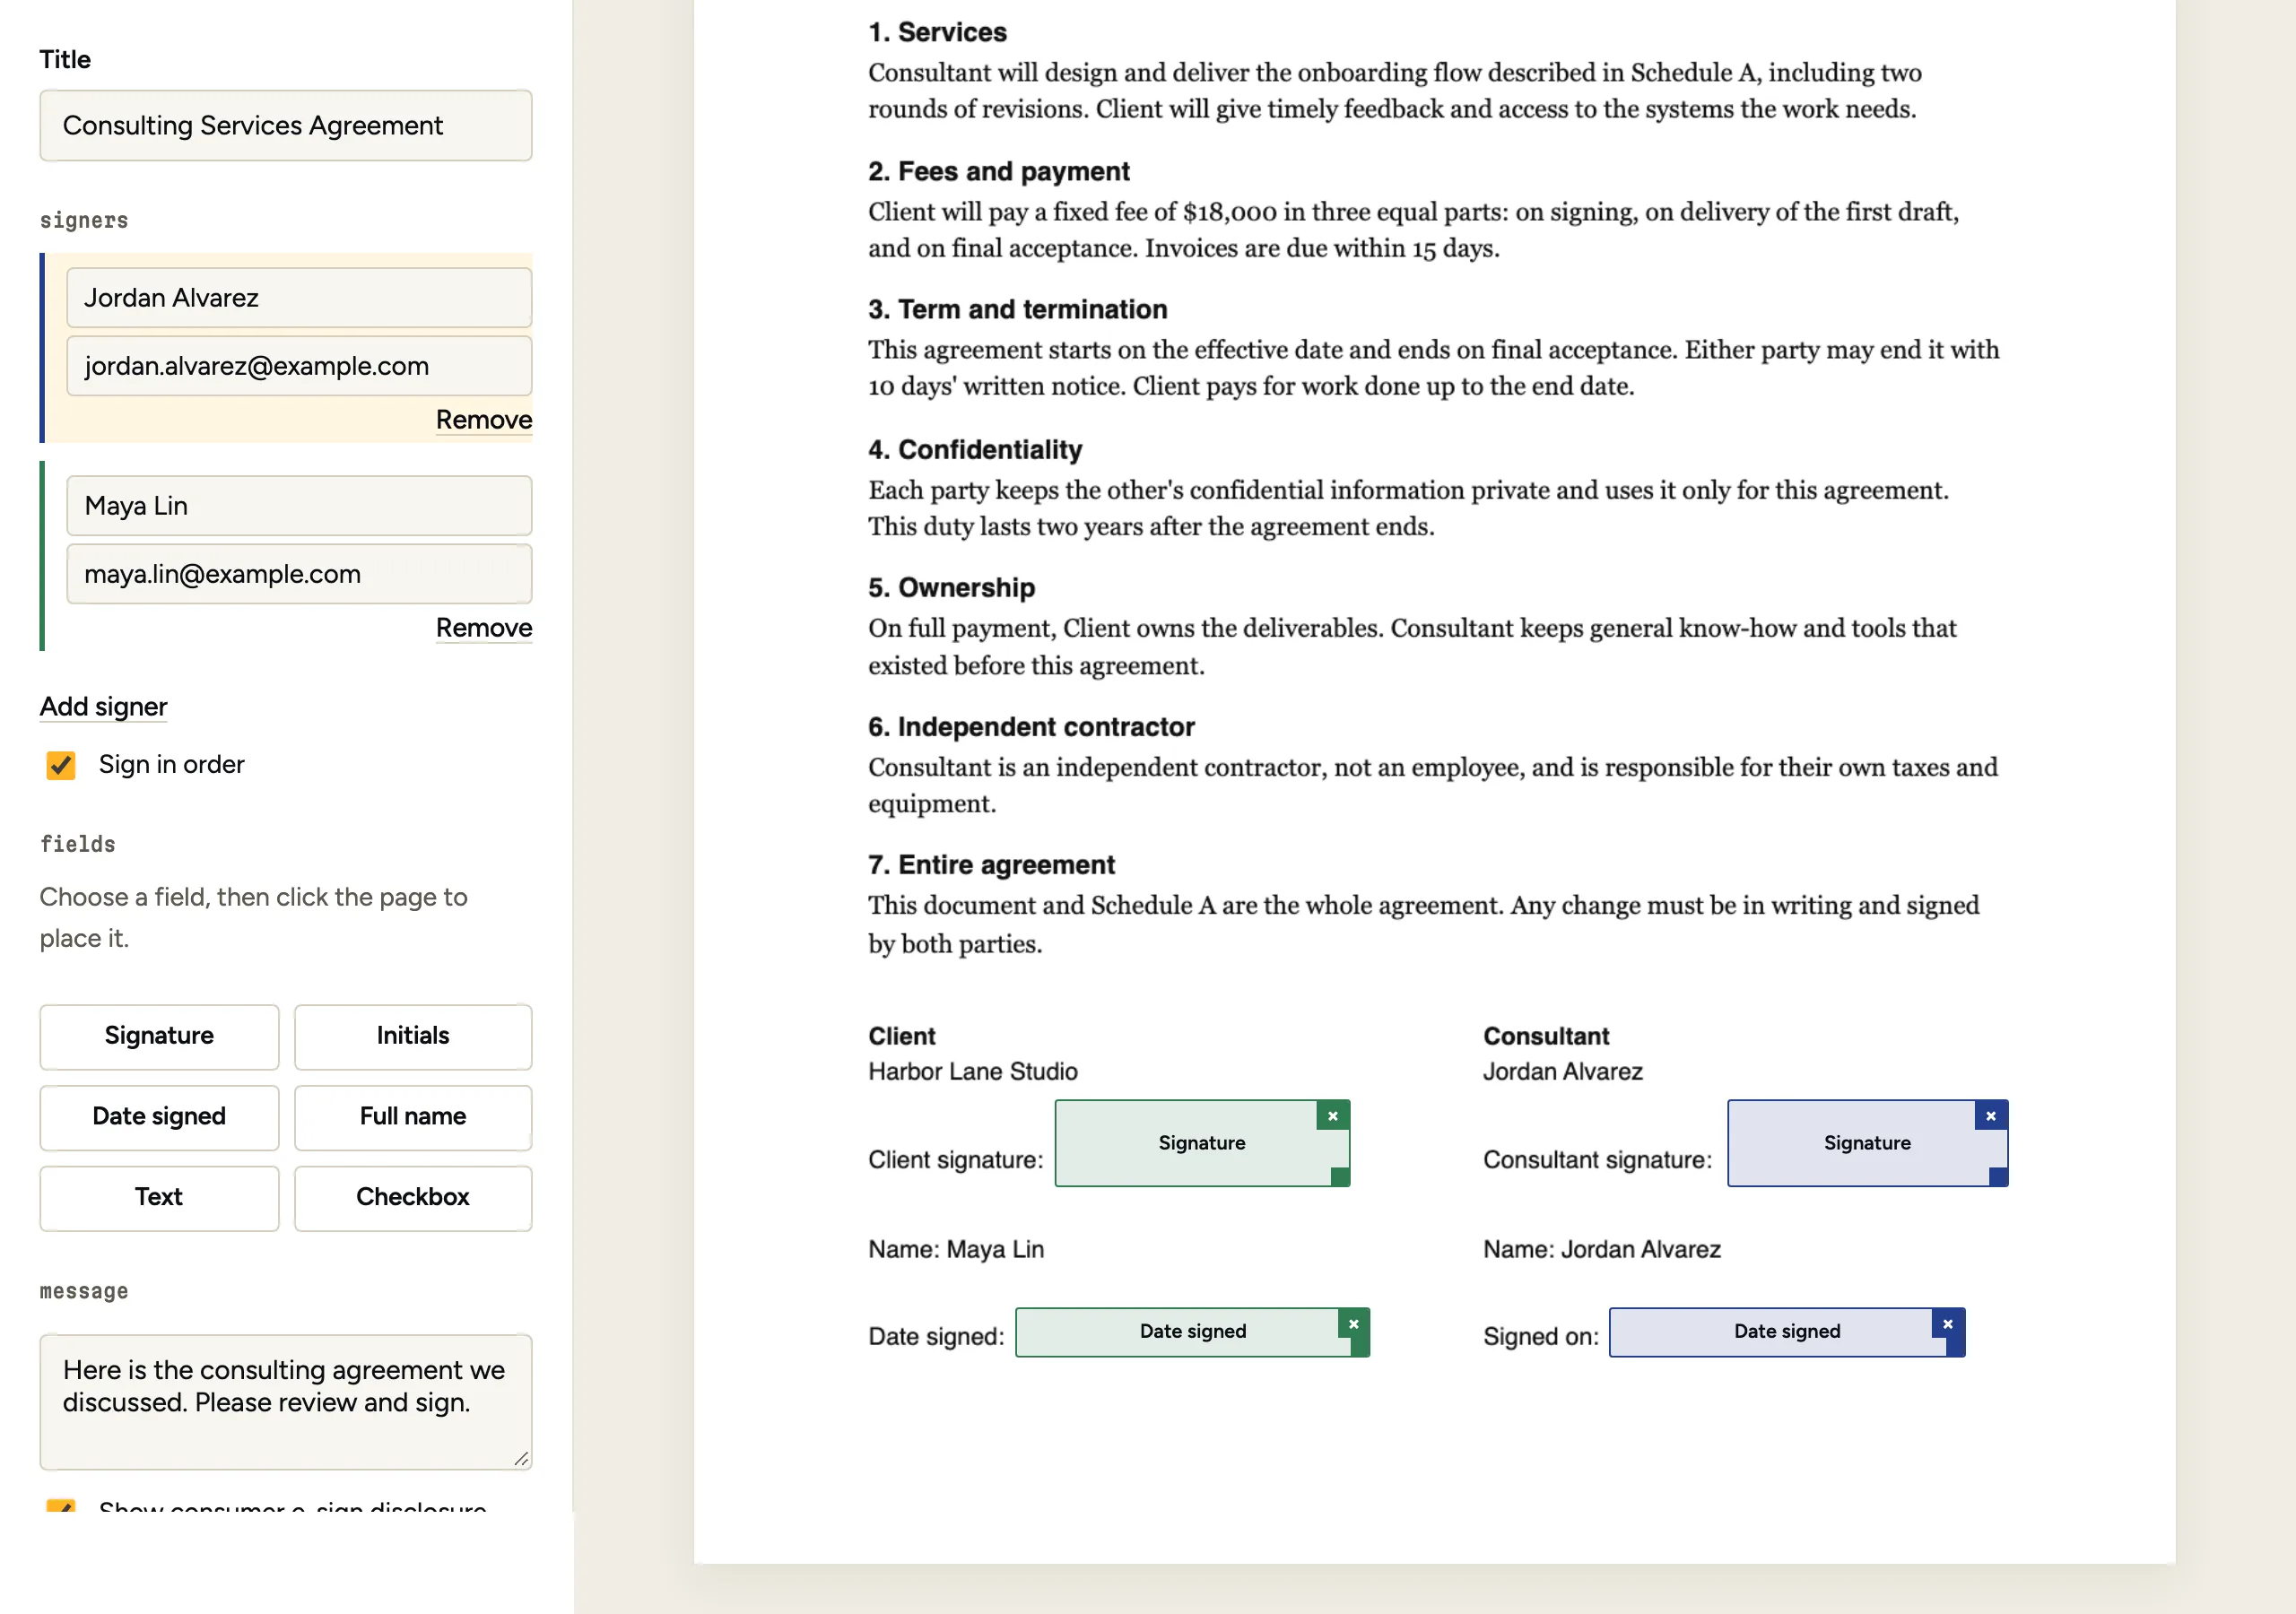
Upload a PDF, drag in fields, send. Your signer gets a link, signs on any phone, and everyone gets a sealed copy.
From an AI agent
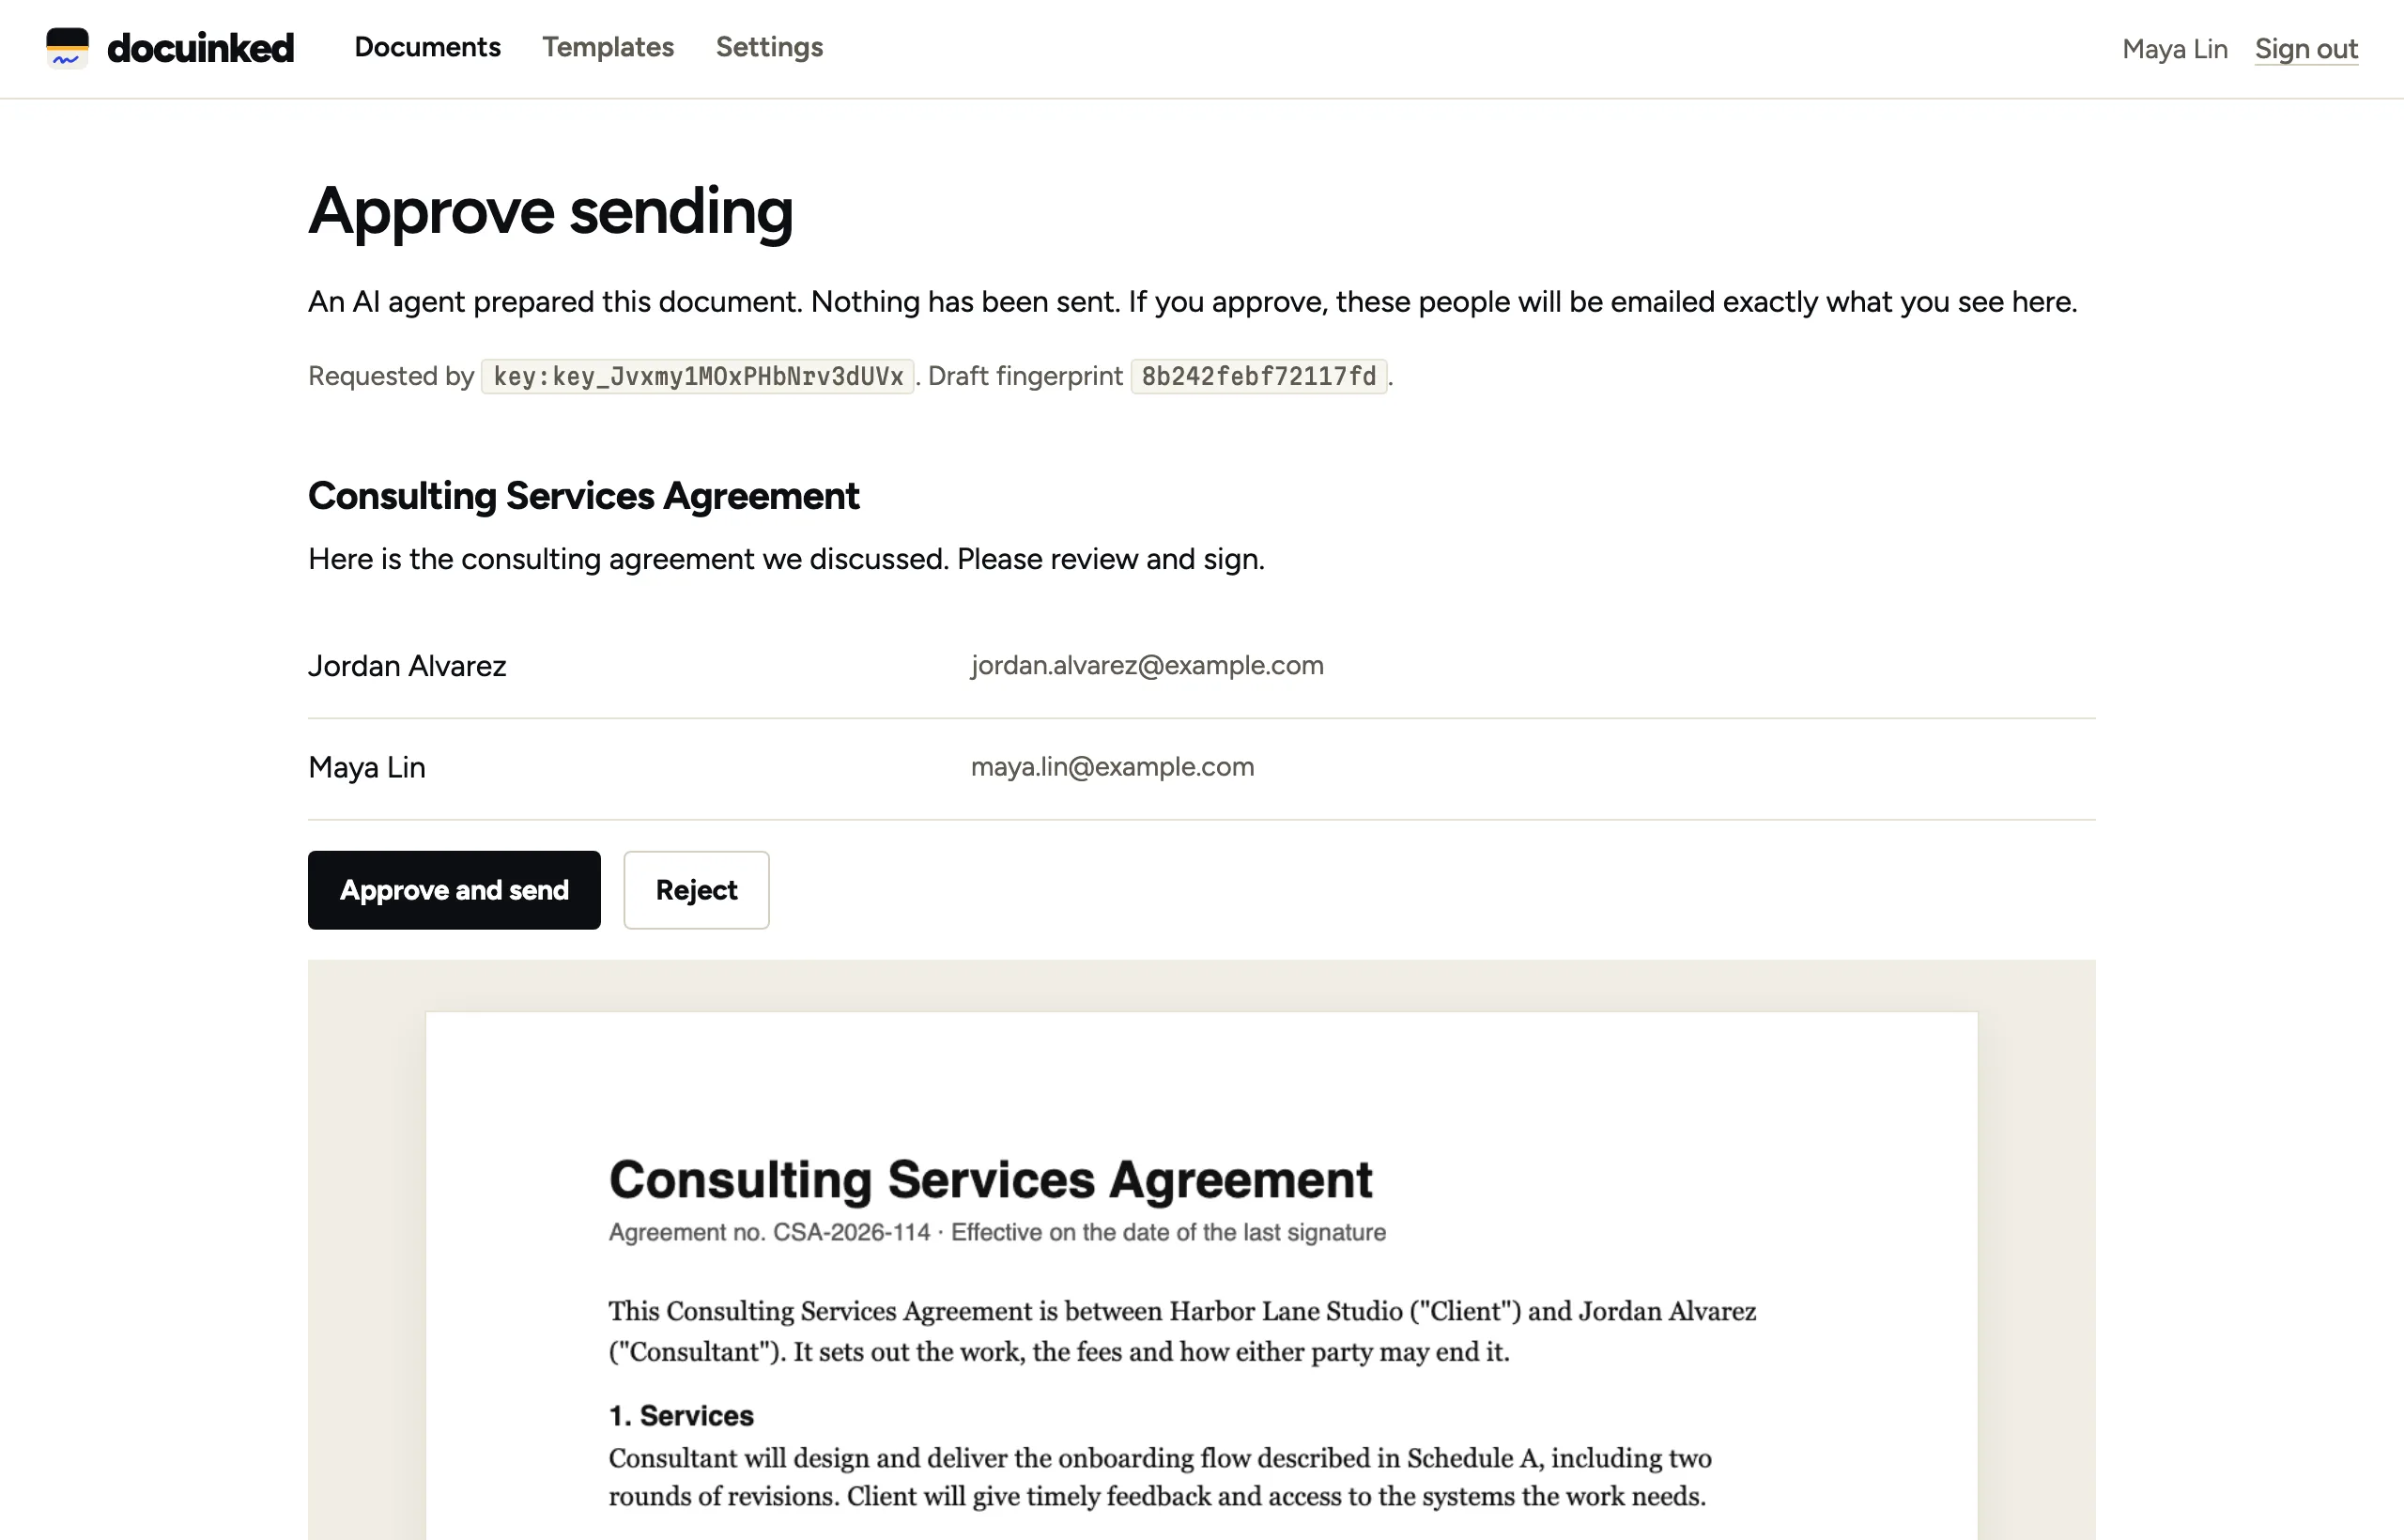
Let Claude or your own agent draft and prepare contracts. It can't send anything until a named person approves the exact draft, and it can never sign.
Inside your product
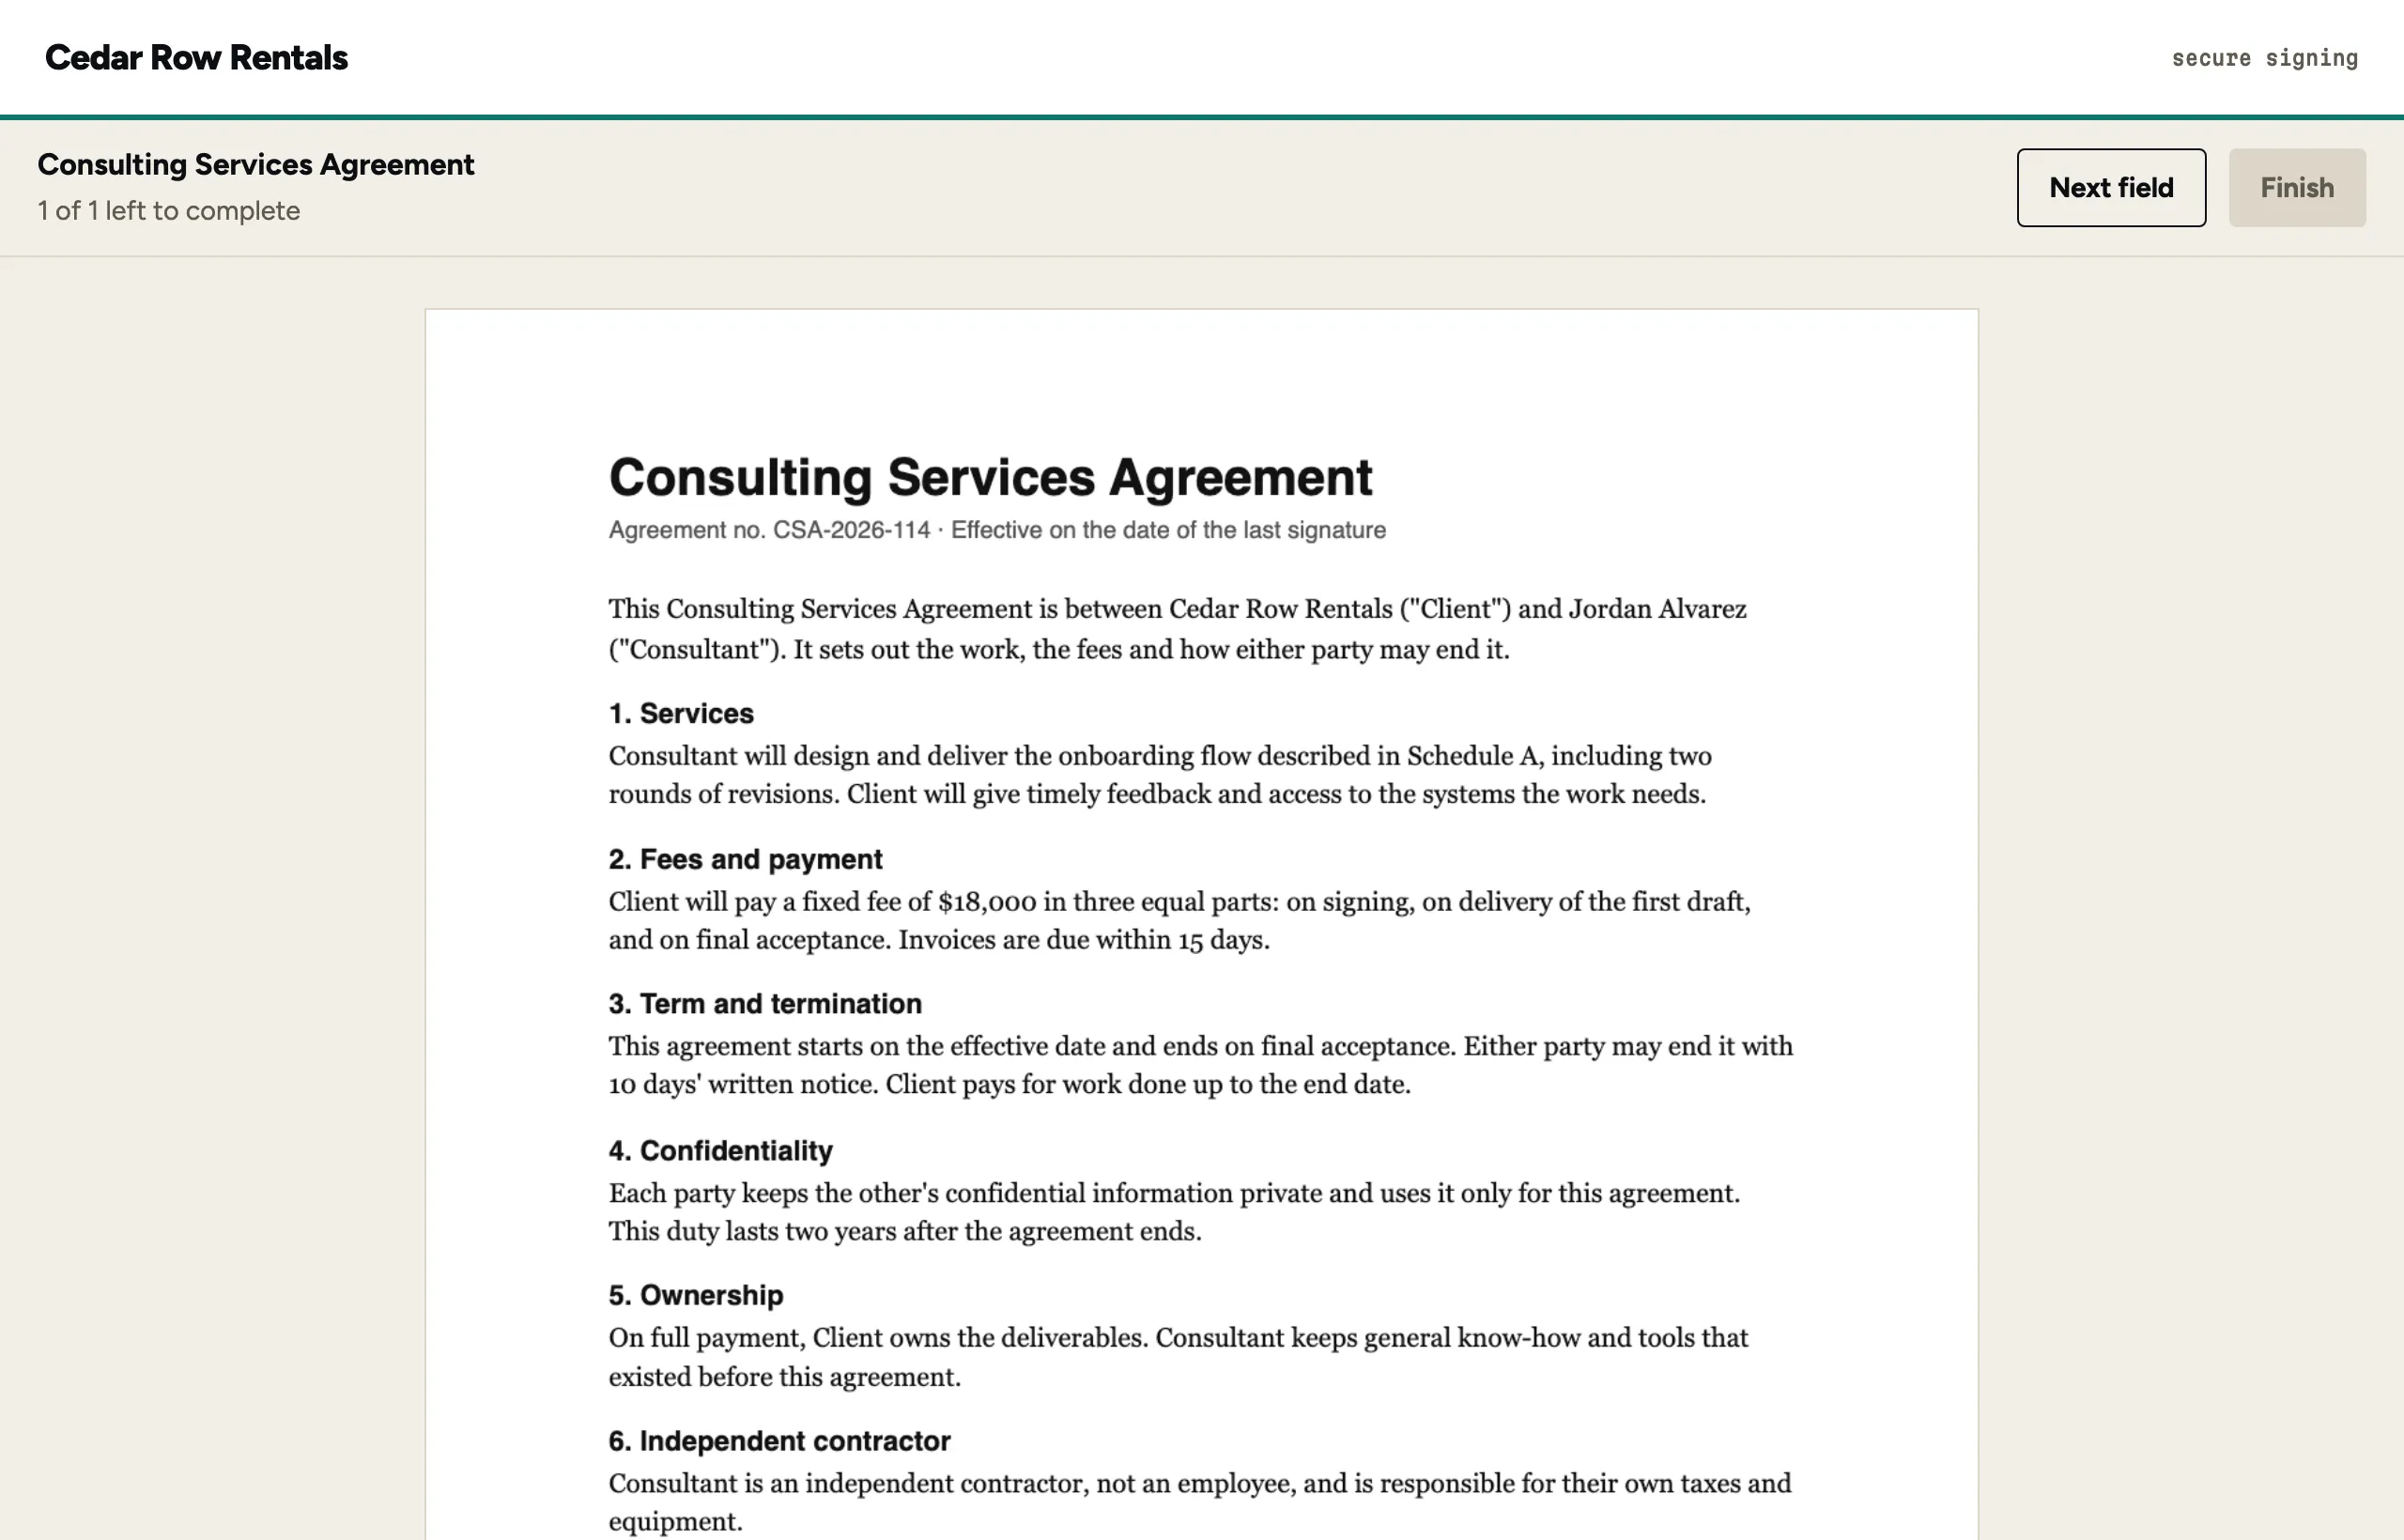
Put signing in your app under your brand. Your logo and colours, embedded signing, and a sub-account for each of your customers.
From PDF to sealed agreement in four steps
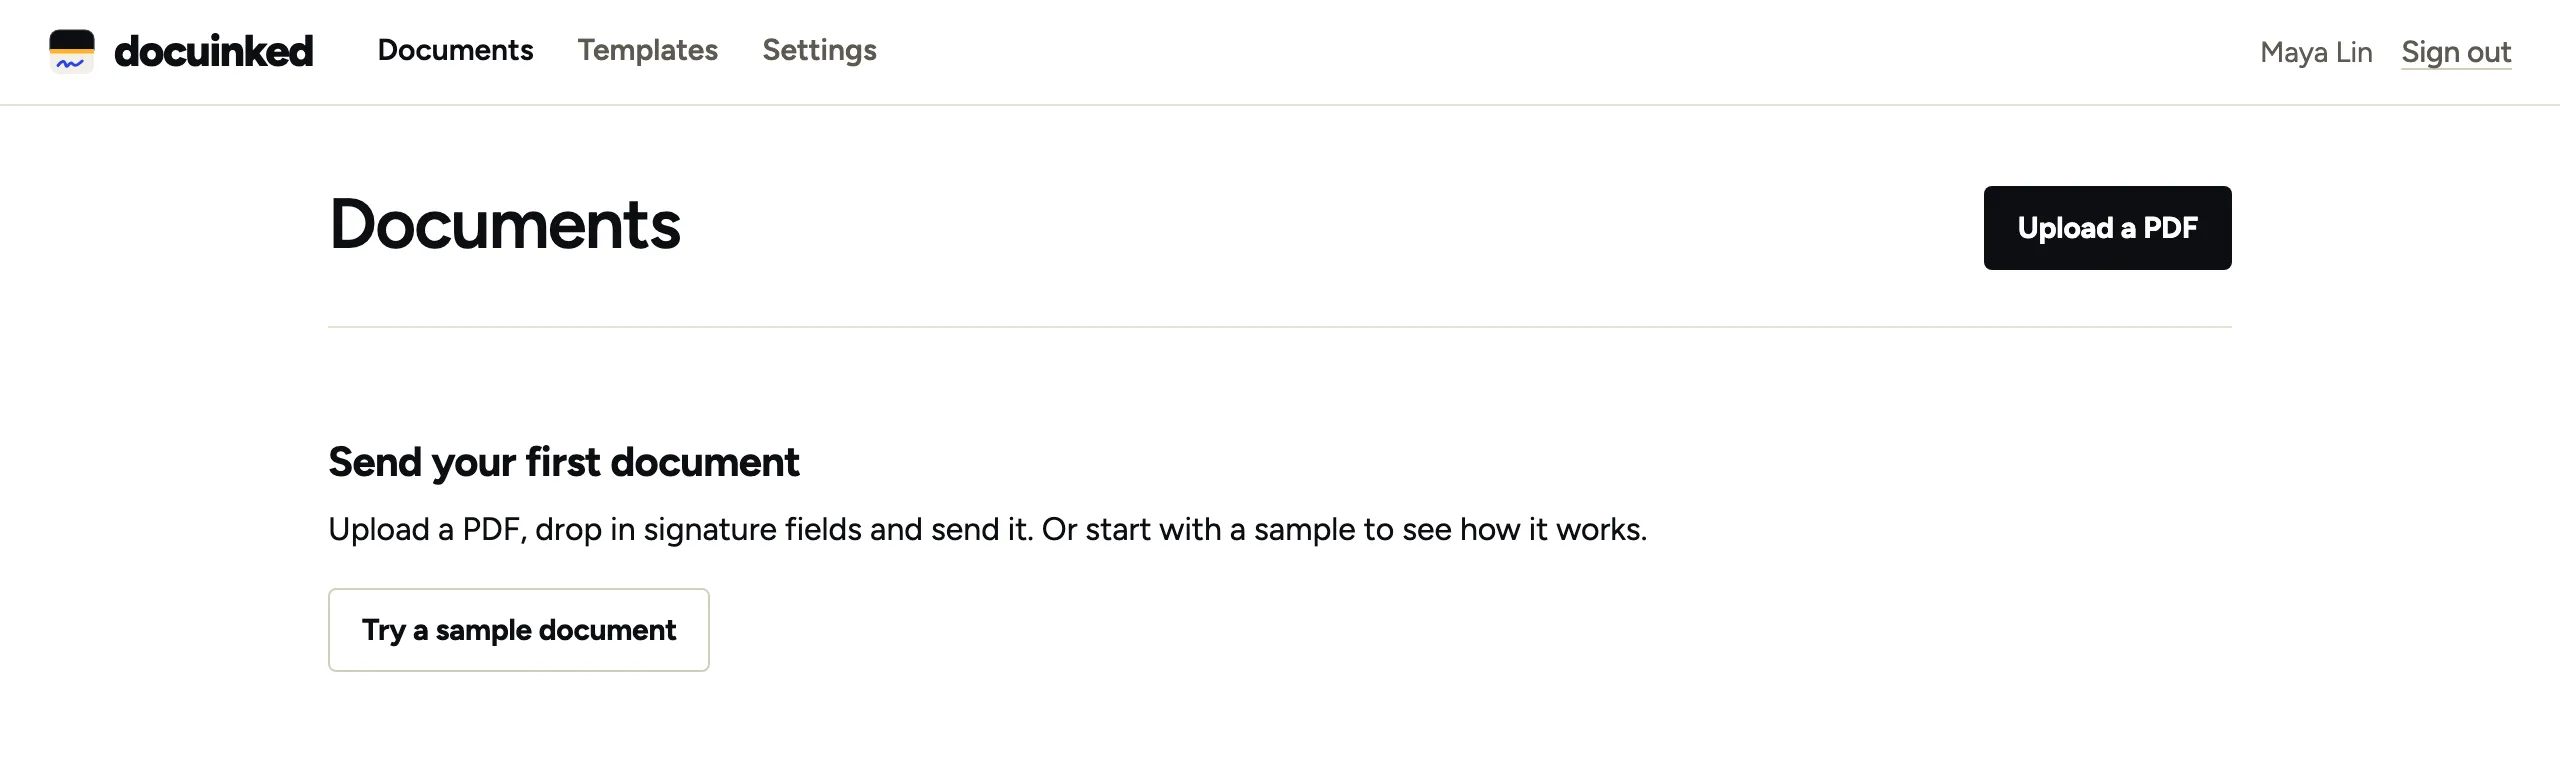
Upload
Drop in any PDF. Or start from a template.
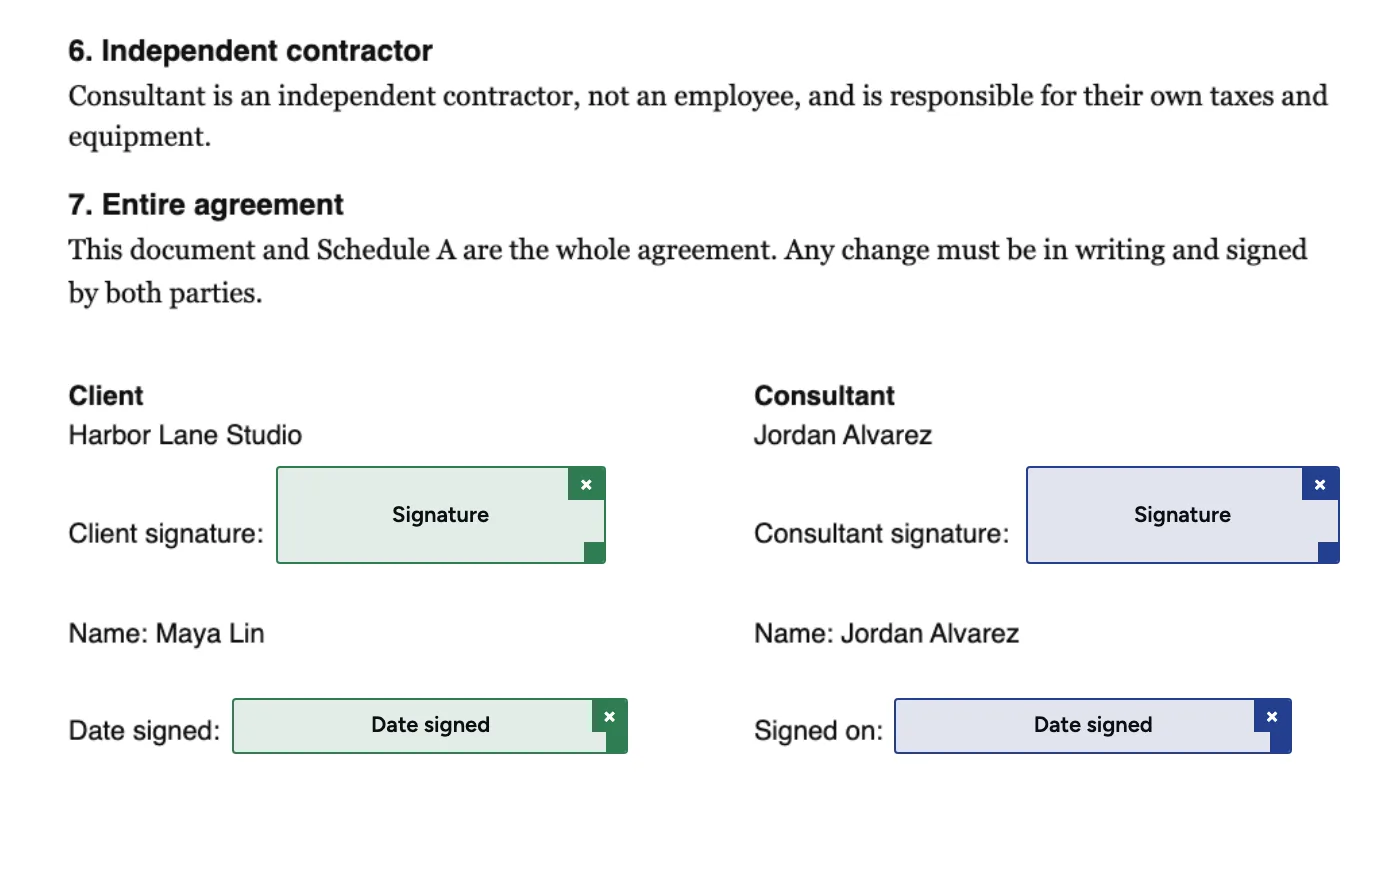
Place fields
Signature, initials, date, text and checkboxes, for each signer. Or let the API place them from text in the PDF.
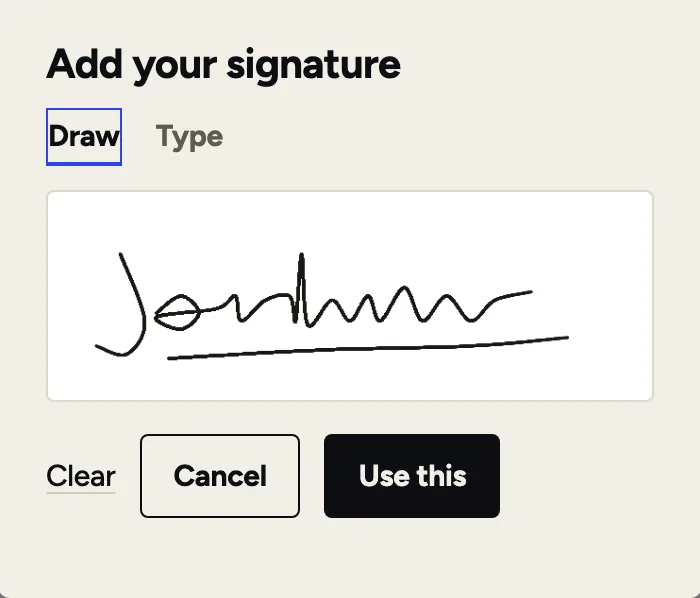
They sign on any device
No account, no app. Signers review, agree and sign in about a minute.
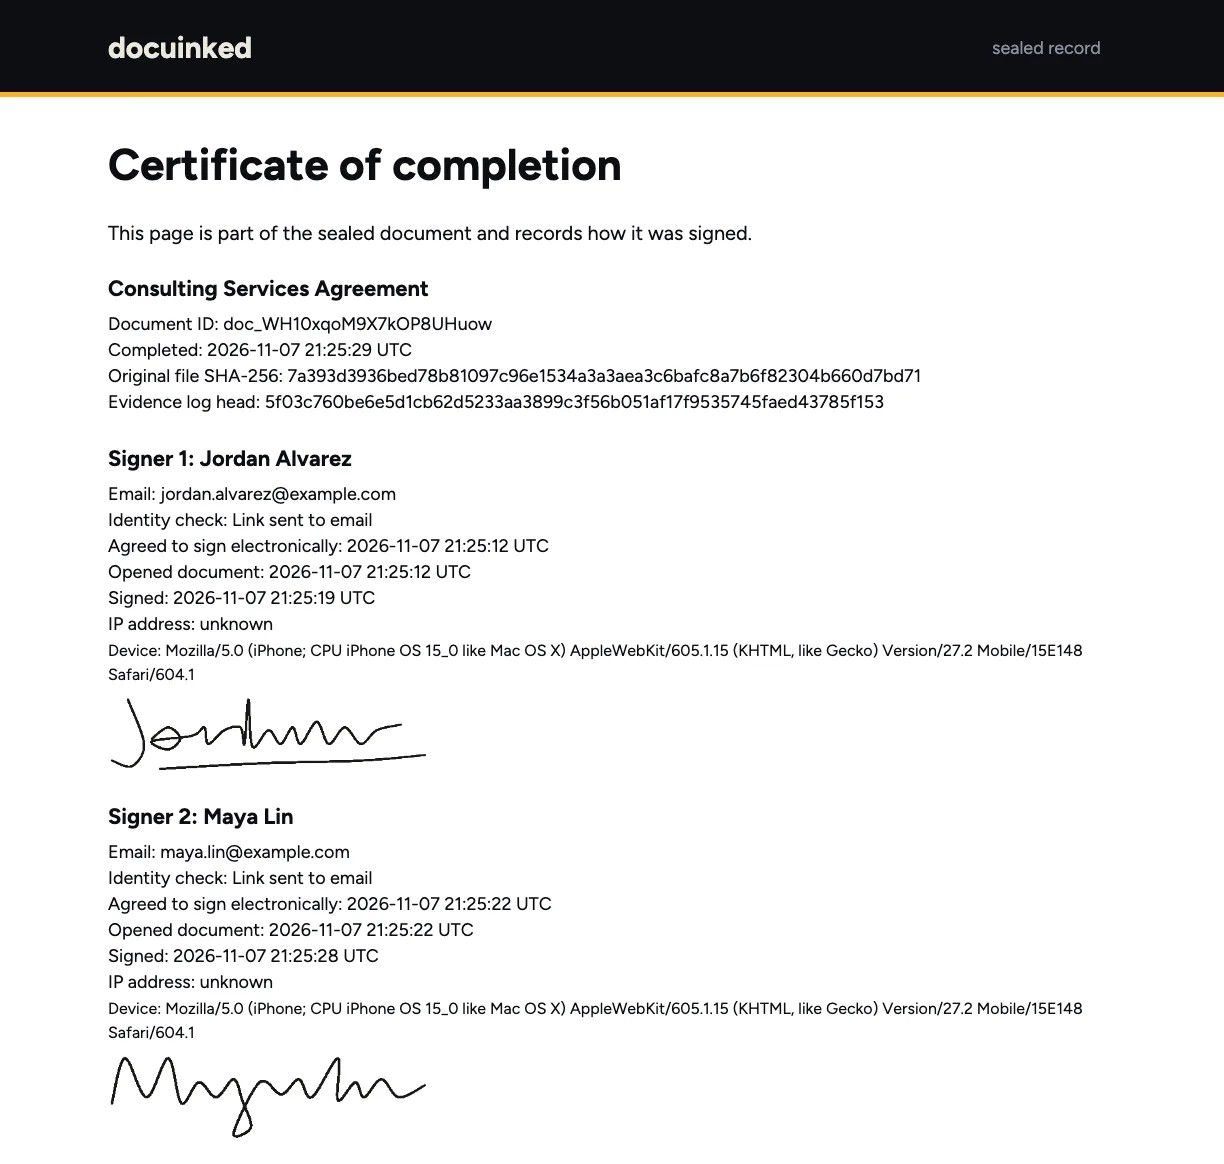
Everyone gets the proof
A sealed PDF with a certificate of completion, plus a full evidence record you can export.
Try it with a sample document (no upload needed)
Everything you need. Nothing you pay extra for.
People, not envelopes
Pay for the people who send: $9 for one, $15 a seat for a team. No envelope counts. Agents, API keys and signers are never seats.
Proof built in
Every completed document carries its own certificate and seal anyone can check.
Your brand, not ours
Show signers your name, logo and colours. Hide ours entirely.
Built for builders
A clean REST API, webhooks, test keys and an MCP server. First signature in minutes.
Safe with AI
Agents prepare. People approve. Only signers sign. Enforced by the server, not a prompt.
Honest by default
We publish what we don't do yet, and we never sell your data.
How docuinked compares
| docuinked | Typical incumbent plans | |
|---|---|---|
| Price to start | First 5 free, then $9 a month | Per-seat plans, often with envelope caps |
| API access | Included | A separate API plan or a higher tier |
| Embedded signing and white-label | Included | Top or enterprise tiers |
| MCP for AI agents | Included | Varies |
| Signer needs an account | No | No |
Details for other products come from their public pricing pages, checked 2026-11-07. They are a better fit if you need SMS or ID checks, bulk send, or audited compliance such as SOC 2. Read the side-by-side comparisons >
Your first signature is one API call
Use a test key and the magic address sign@test.docuinked.com. The document signs itself, so you see the whole flow without emailing anyone.
curl https://docuinked.com/v1/documents \
  -H "Authorization: Bearer $DOCUINKED_API_KEY" \
  -H "Idempotency-Key: quickstart-1" \
  -H "Content-Type: application/json" \
  -d '{"title": "Test NDA",
       "pdf_url": "https://docuinked.com/docs/sample.pdf",
       "signers": [{"name": "Test Signer",
                    "email": "sign@test.docuinked.com"}],
       "send": true}'
{"status": "ok",
"data": {
"id": "doc_T74KbLR3QeBWkhW1eZ2B",
"status": "sealing",
"test": true,
"signers": [{"name": "Test Signer",
"status": "signed"}],
"next_action": "Test mode: no email was sent. ..."}}Built to be trusted with your agreements
A signed agreement is only as good as the record behind it. So every document is protected while it waits, and sealed with its evidence when it is done.
- Encryption. Every stored PDF is encrypted with AES-256-GCM and bound to its document.
- Seal and timestamp. Finished PDFs get a PAdES seal and a timestamp from an outside authority. Any later change breaks the seal.
- Hash-chained evidence. Each step is chained to the one before, and the log refuses edits.
- Access controls. Two-factor sign-in, keys stored only as hashes, and agent keys that can never sign.
We're in public beta. We don't have a SOC 2 report yet, and we say so.